Cloudflare Tunnel 实现内网穿透

#cloudflare-tunnel #reverse-proxy #zero-trust

Prepare work

  • Cloudflare Account
  • A Domain name which register under Cloudflare

Setup steps

Cloudflare Dashboard –> Zero Trust –> Networks –>Tunnels-> Create new Tunnels –> Connector(Cloudflared)
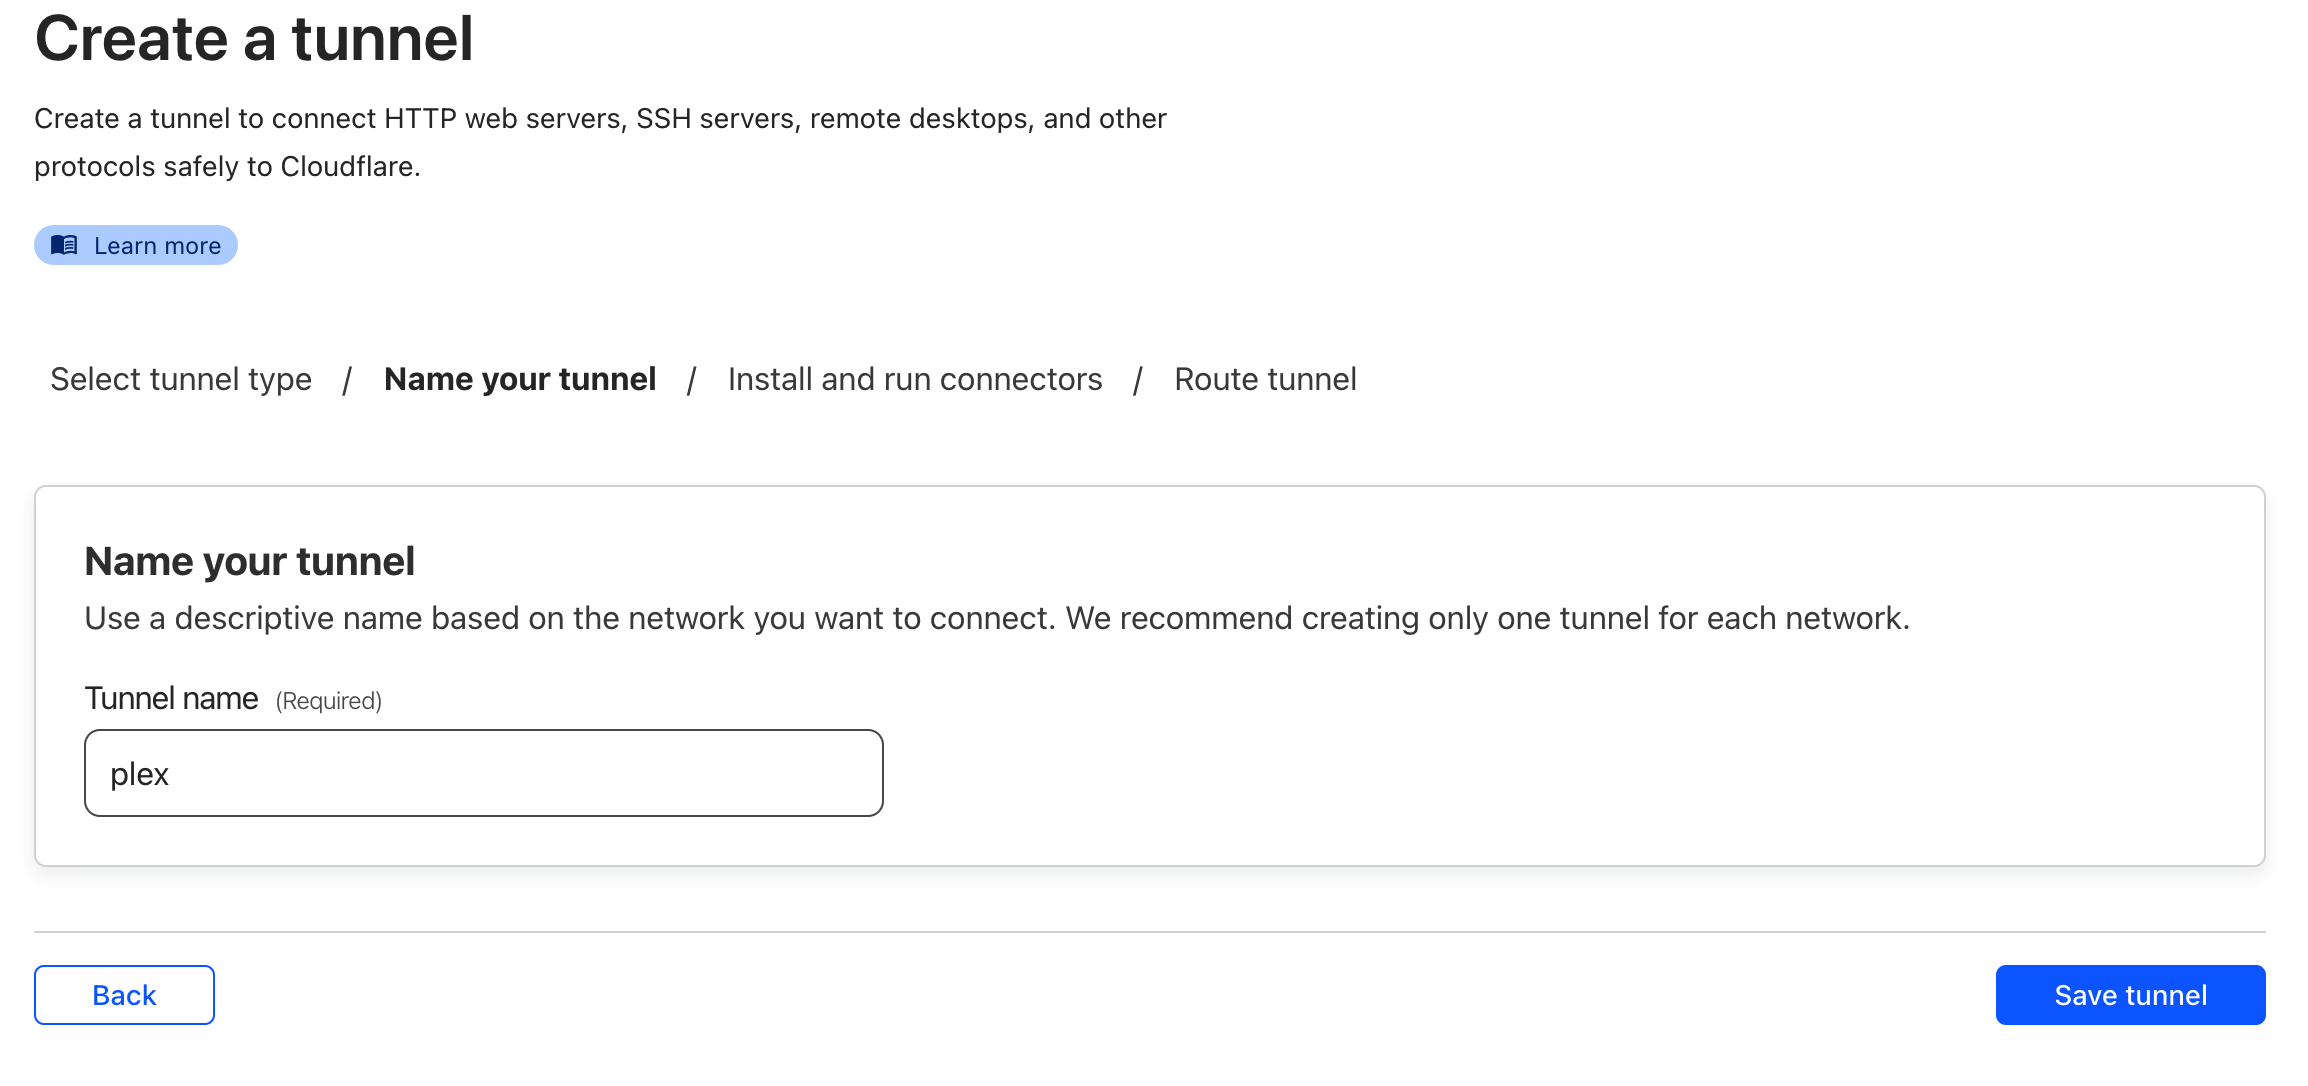
image-20240509164856584

Tips

If you have multiple applications on one server, recommend use docker to create multiple connectors for each Application. Here are using Docker for example .
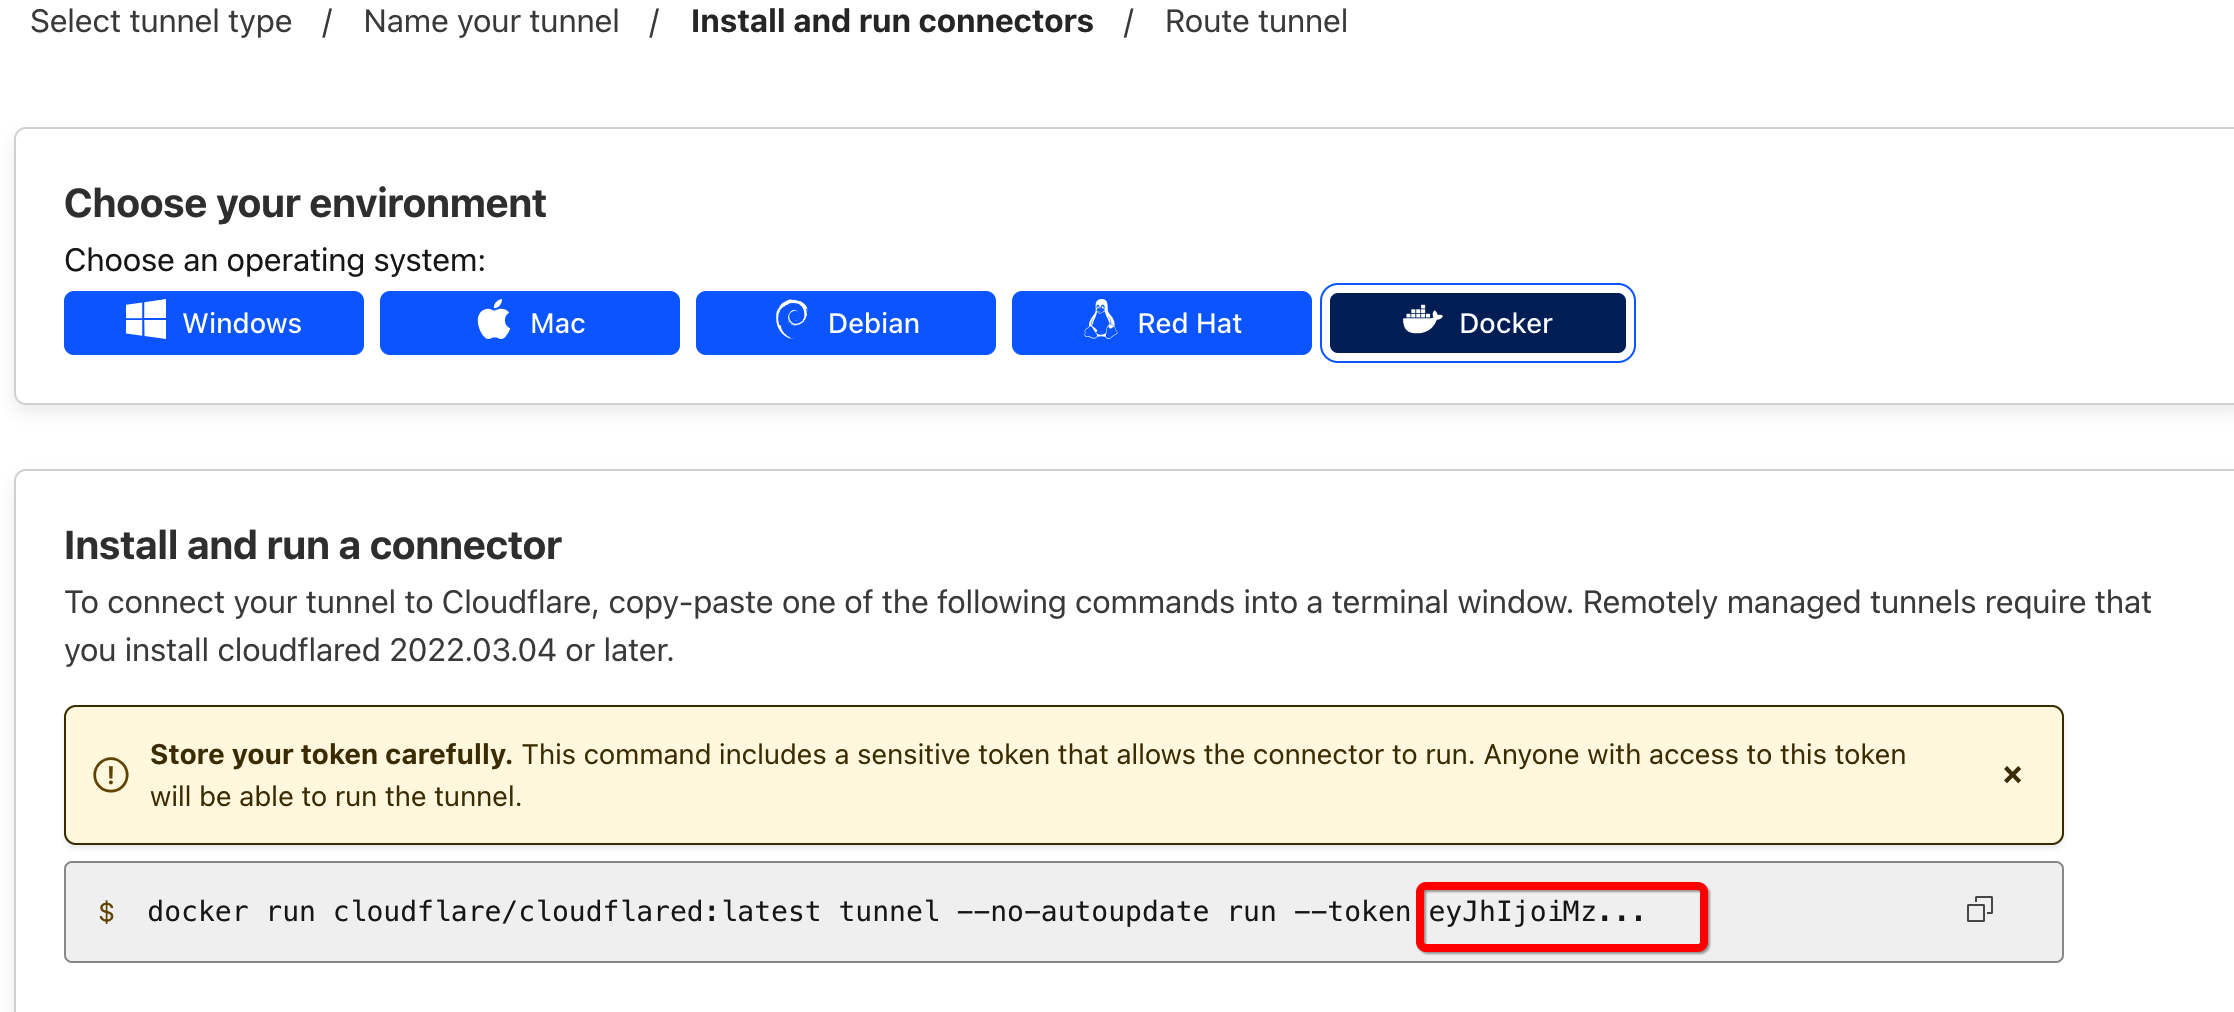
image-20240509165511577

Copy the application token and save it to docker-compose.yml:

# service description
services:
cloudflare-tunnel:
image: cloudflare/cloudflared
container_name: cloudflare-tunnel-plex
hostname: cloudflare-tunnel
restart: unless-stopped
network_mode: "host"
command: tunnel run
dns:
- '192.168.3.1'
volumes:
- /etc/localtime:/etc/localtime:ro
- /etc/hosts:/etc/hosts
environment:
- "TUNNEL_TOKEN=${TOKEN}" # Your Token Here
labels:
# enbale watchtower updates
- "com.centurylinklabs.watchtower.enable=true"
[root@home ~/cloudflared-proxy/plex]# docker-compose up -d
[+] Running 1/1
✔ Container cloudflare-tunnel-plex Started

image-20240509170300189

Connectors that is becomes healthy. That means we successfully connected. Then we go to the next step to set proxy.
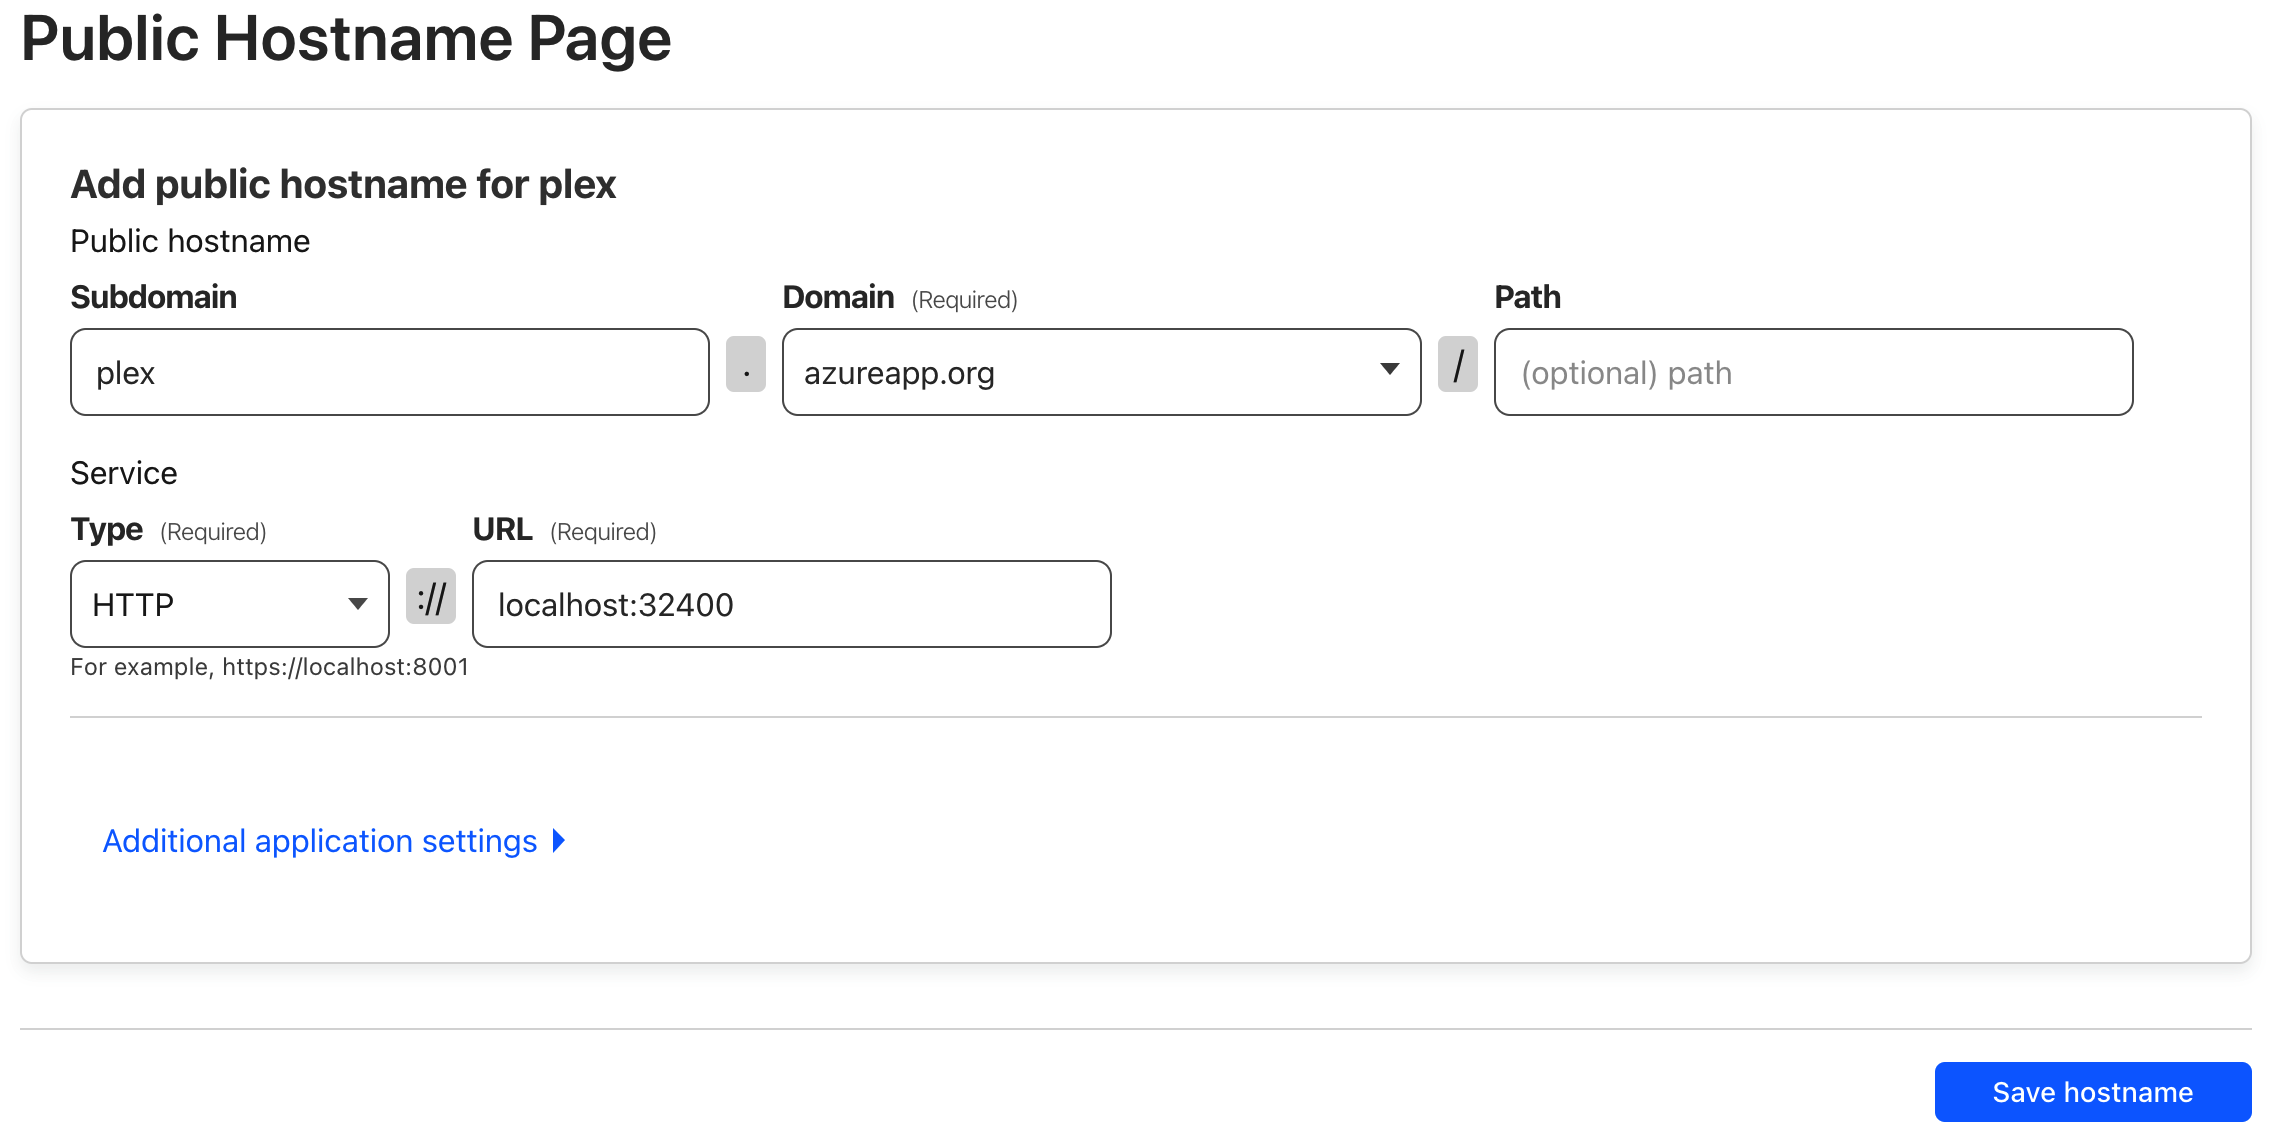
image-20240509170848133

[root@home ~/cloudflared-proxy/plex]# nslookup plex.azureapp.org
Server: 192.168.3.1
Address: 192.168.3.1#53

Non-authoritative answer:
Name: plex.azureapp.org
Address: 172.67.136.8
Name: plex.azureapp.org
Address: 104.21.54.63

Now we can access http://localhost:32400 the plex from lan network and access https://plex.azureapp.org from public network.
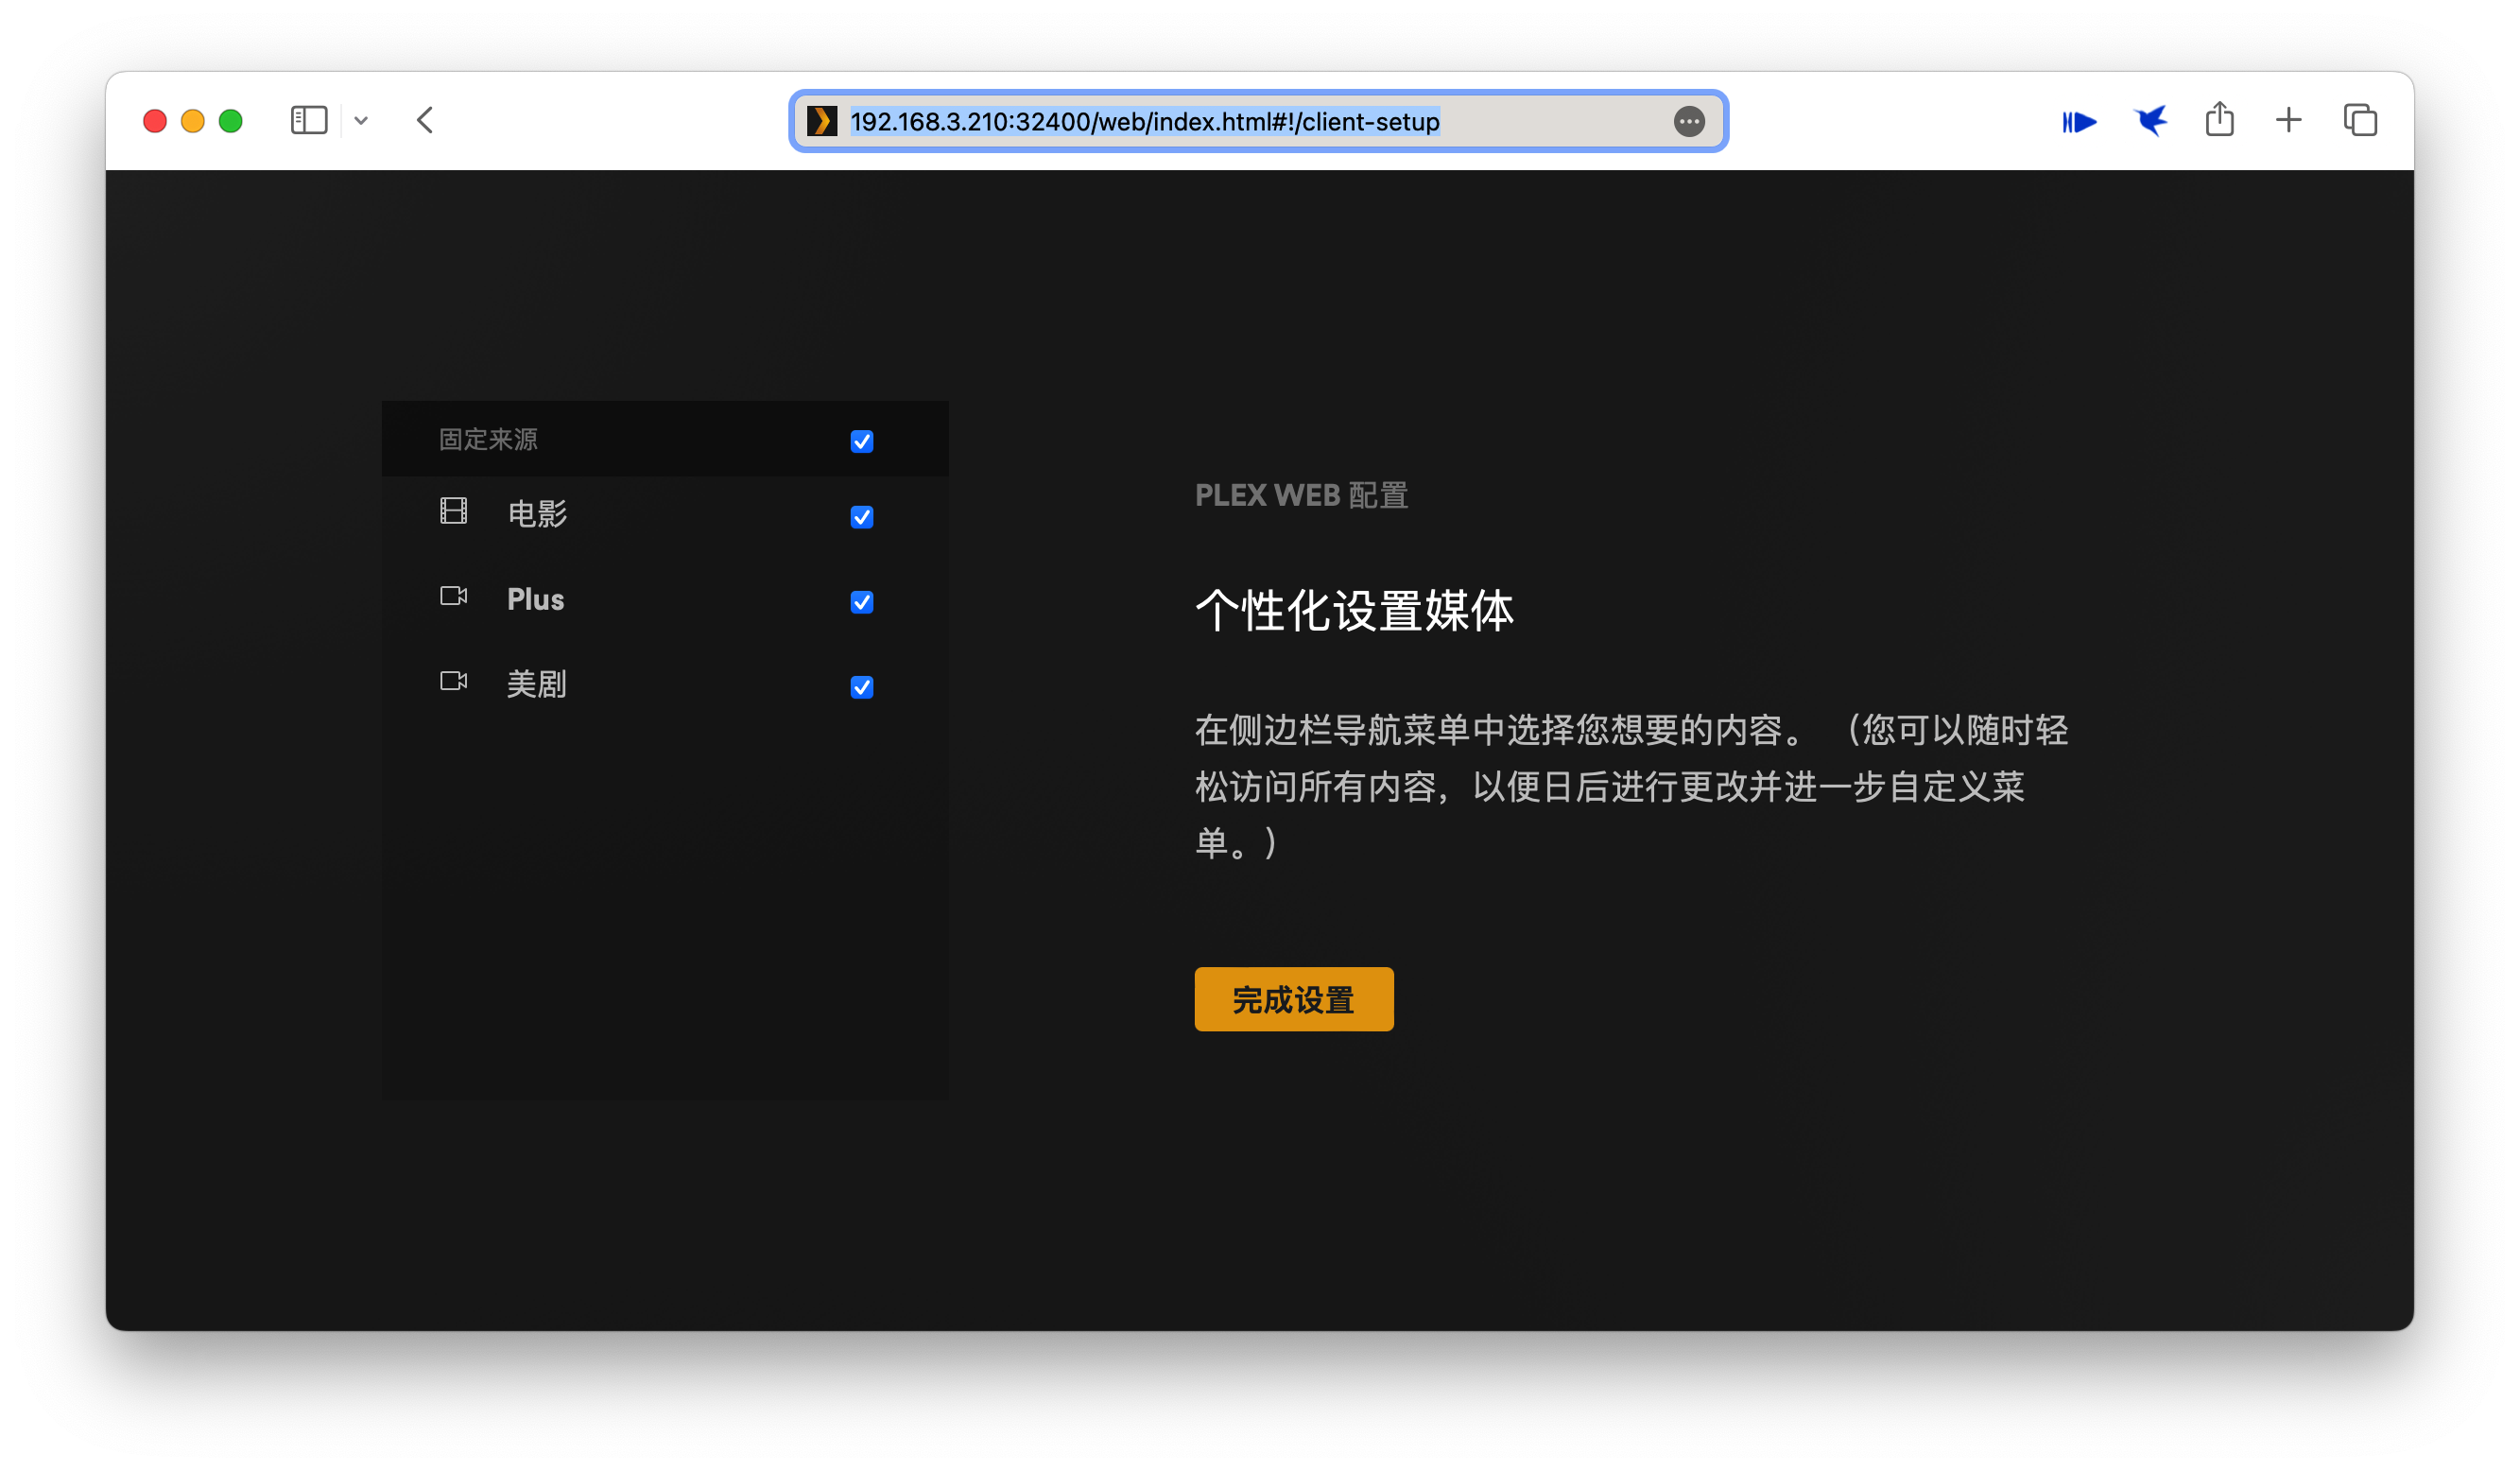
image-20240509171519755
